# Heartbleed Openssl Bug
**URL:** https://forums.speedlife.net/t/heartbleed-openssl-bug/268950
**Category:** NYSpeed Off Topic
**Created:** [April 7, 2014, 5:26pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950 "2014-04-07T17:26:50Z")
**Posts on this page:** 20
**Page:** 4
### Author:  [@boxxa](https://forums.speedlife.net/u/boxxa)
#### Post date: [April 10, 2014, 8:43am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/61 "2014-04-10T08:43:21Z")
> [@LZ](#):
>
> You might be able to get it when a process forks
>
> It’s just odd some security people are running around say all these private keys are lost
I don’t think so. Master thread loads SSL certs, childs connect to master thread so I think the key would already be loaded and passed on. Seems like this would squeeze the memory.
You would need to crash a HTTP server and force the restart while capturing for a private key to get dumped. Not 100% sure but don’t see how loading private keys every time there was a child would be the best memory usage.
---
### Author:  [@boardjnky4](https://forums.speedlife.net/u/boardjnky4)
#### Post date: [April 10, 2014, 9:14am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/62 "2014-04-10T09:14:30Z")
> [@LZ](#):
>
> You might be able to get it when a process forks
>
> It’s just odd some security people are running around say all these private keys are lost
Some people just like to feel important by causing panic.
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 10, 2014, 9:23am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/63 "2014-04-10T09:23:45Z")
> [@boxxa](#):
>
> I don’t think so. Master thread loads SSL certs, childs connect to master thread so I think the key would already be loaded and passed on. Seems like this would squeeze the memory.
>
> You would need to crash a HTTP server and force the restart while capturing for a private key to get dumped. Not 100% sure but don’t see how loading private keys every time there was a child would be the best memory usage.
I get all that I was just trying to figure out some angle to cause all the panic 🙂
A lot of places are advising everyone to get all new certs
---
### Author:  [@boardjnky4](https://forums.speedlife.net/u/boardjnky4)
#### Post date: [April 10, 2014, 9:24am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/64 "2014-04-10T09:24:49Z")
LZ wanted to publish [yahoo.com](http://yahoo.com)’s private key on pastebin
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 10, 2014, 9:32am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/65 "2014-04-10T09:32:38Z")
This bug is going to be super useful for years to come on internal assessments.
All kinds of internal apps for companies never update this shit and once you have creds its usually easy to elevate privileges or find some other bug.
---
### Author:  [@JayS](https://forums.speedlife.net/u/JayS)
#### Post date: [April 10, 2014, 10:26am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/66 "2014-04-10T10:26:14Z")
> **[Change these passwords right now](http://money.cnn.com/2014/04/10/technology/security/heartbleed-passwords/index.html?hpt=hp_t2)**
>
> Worried about the Heartbleed bug? Here are the passwords to change immediately.
^ Shows some of the big ones affected and lists if they’re patched yet or not.
Just got done changing my gmail, yahoo and facebook passwords.
---
### Author:  [@boxxa](https://forums.speedlife.net/u/boxxa)
#### Post date: [April 10, 2014, 11:06am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/67 "2014-04-10T11:06:01Z")
> [@LZ](#):
>
> I get all that I was just trying to figure out some angle to cause all the panic 🙂
>
> A lot of places are advising everyone to get all new certs
It isn’t. There was the mass hysteria that it was possible and yes, it was but the only shot it would leak is on a reboot or the quick instant that it is allocated to memory. No company would want to be the one that didn’t change their private keys and be blamed if they were the 0.001% that maybe leaked them.
malloc() dumps recent memory so you aren’t really getting SSL keys even right after a web server reboot or system reboot. The memory heap is used for something else pretty quickly so from a web server, you are getting user sessions and usernames that are passed for the most recent connections in 64k chunks. Some apps may be better at exploiting the SSL keys depending on how they are written tho as there may not be as much memory writing depending on what they are doing. Small app on big server could mean trouble. Can test this pretty simple with a small NodeJS app. Run it with SSL turned on, just output text and see if you can dump the key.
Either way, the bug is pretty cool how it works and dumb programming for sure.
> [@JayS](#):
>
> [Heartbleed bug: passwords to change right now](http://money.cnn.com/2014/04/10/technology/security/heartbleed-passwords/index.html?hpt=hp_t2)
>
> ^ Shows some of the big ones affected and lists if they’re patched yet or not.
>
> Just got done changing my gmail, yahoo and facebook passwords.
Two factor auth is your friend. May know my Gmail password but still need my phone every login.
---
### Author:  [@boardjnky4](https://forums.speedlife.net/u/boardjnky4)
#### Post date: [April 10, 2014, 11:10am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/68 "2014-04-10T11:10:42Z")
We’re getting all new Certs issued on affected machines. We hammered our vendor with requests.
---
### Author:  [@boxxa](https://forums.speedlife.net/u/boxxa)
#### Post date: [April 10, 2014, 11:25am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/69 "2014-04-10T11:25:50Z")
> [@boardjnky4](#):
>
> We’re getting all new Certs issued on affected machines. We hammered our vendor with requests.
Did you regenerate your CSRs or just the reissue for the cert?
I just spent a night going through 38 servers patching SSL and regenerating certs. My god are the providers getting hammered with requests.
---
### Author:  [@boardjnky4](https://forums.speedlife.net/u/boardjnky4)
#### Post date: [April 10, 2014, 11:53am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/70 "2014-04-10T11:53:57Z")
I believe our instructions to the application owners was to re-generate AND re-sign. Most people just follow the KB article that we have posted which instructs the user to generate the CSR, so they’re probably doing that even if they don’t realize it.
---
### Author:  [@boxxa](https://forums.speedlife.net/u/boxxa)
#### Post date: [April 10, 2014, 12:16pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/71 "2014-04-10T12:16:27Z")
> [@boardjnky4](#):
>
> I believe our instructions to the application owners was to re-generate AND re-sign. Most people just follow the KB article that we have posted which instructs the user to generate the CSR, so they’re probably doing that even if they don’t realize it.
Ya probably. One the risk was that everything was leaked, I would imagine the notice was to regenerate everything. Lol.
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 10, 2014, 12:19pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/72 "2014-04-10T12:19:18Z")
Such a cluster fuck
I’m curious if people are auditing the fuck out of OpenSSL now.
---
### Author:  [@boardjnky4](https://forums.speedlife.net/u/boardjnky4)
#### Post date: [April 10, 2014, 12:22pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/73 "2014-04-10T12:22:18Z")
> [@boxxa](#):
>
> Ya probably. One the risk was that everything was leaked, I would imagine the notice was to regenerate everything. Lol.
Yeah we let the server guys make the announcement to the users that were impacted since they were the ones communicating the patch process. We (infosec) spent most of our time identifying machines affected and making sure they were in the patch process.
---
### Author:  [@TradersBASE](https://forums.speedlife.net/u/TradersBASE)
#### Post date: [April 10, 2014, 12:37pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/74 "2014-04-10T12:37:22Z")
> [@LZ](#):
>
> Such a cluster fuck I’m curious if people are auditing the fuck out of OpenSSL now.
This tied up a bunch of my time yesterday, thanks Obama!
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 10, 2014, 4:21pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/75 "2014-04-10T16:21:23Z")
Work smashed together a bunch of the information - [http://accuvantstorage.blob.core.windows.net/web/file/2016b4dc040c49ee991b5721e0dd62b3/HeartBleed-Bug-CVE-2014-0160-release.pdf](http://accuvantstorage.blob.core.windows.net/web/file/2016b4dc040c49ee991b5721e0dd62b3/HeartBleed-Bug-CVE-2014-0160-release.pdf)
---
### Author:  [@ProgRocker](https://forums.speedlife.net/u/ProgRocker)
#### Post date: [April 11, 2014, 7:12am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/76 "2014-04-11T07:12:32Z")
Yahoo compromised? Millions of spammers and old people must be panicking
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 11, 2014, 10:28am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/77 "2014-04-11T10:28:15Z")
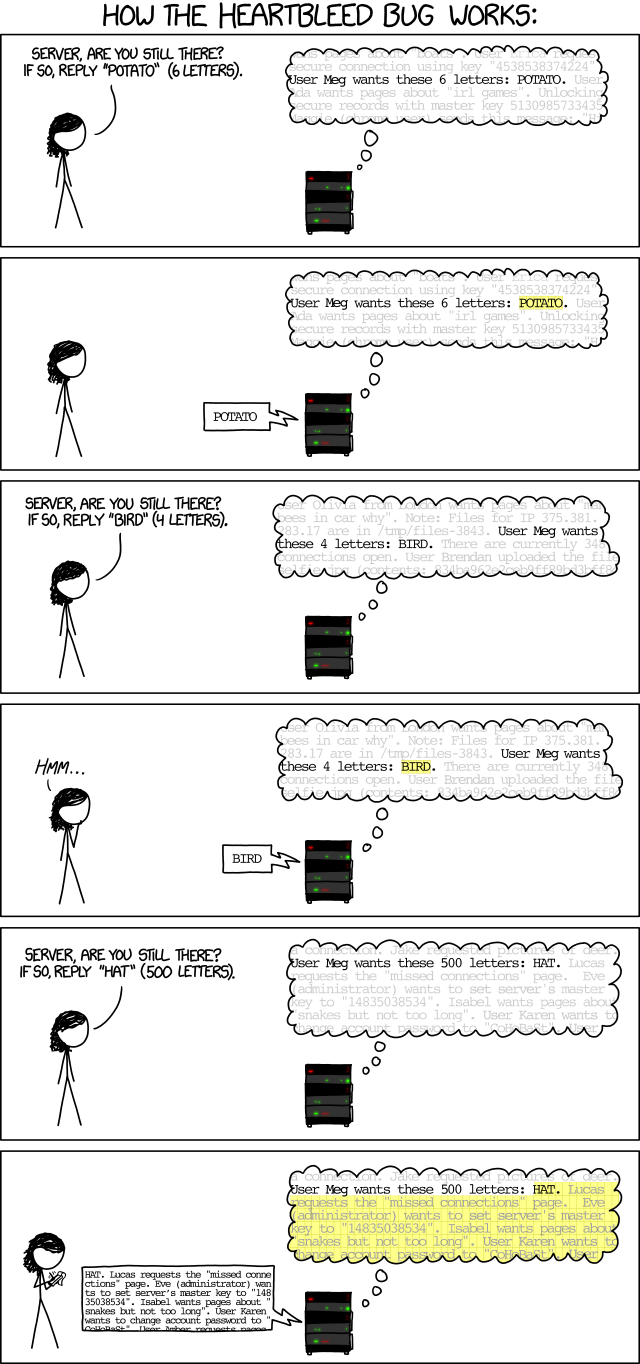
This will help the people who suck at computers
---
### Author:  [@ProgRocker](https://forums.speedlife.net/u/ProgRocker)
#### Post date: [April 11, 2014, 11:04am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/78 "2014-04-11T11:04:27Z")
Here’s the fix for those who suck at computers:
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 11, 2014, 12:47pm UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/79 "2014-04-11T12:47:19Z")
Nice - [http://www.bloomberg.com/news/2014-04-11/nsa-said-to-have-used-heartbleed-bug-exposing-consumers.html](http://www.bloomberg.com/news/2014-04-11/nsa-said-to-have-used-heartbleed-bug-exposing-consumers.html) ****
---
### Author:  [@LZ1](https://forums.speedlife.net/u/LZ1)
#### Post date: [April 12, 2014, 5:07am UTC](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950/80 "2014-04-12T05:07:57Z")
I guess that answers that - [https://www.cloudflarechallenge.com/heartbleed](https://www.cloudflarechallenge.com/heartbleed)
However the server was rebooted during testing
[Previous page](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950.md?page=3)
[Next page](https://forums.speedlife.net/t/heartbleed-openssl-bug/268950.md?page=5)